Managed IT
8 Signs You Need Managed IT and Cybersecurity
The eight signs below indicate your business is ready for that shift. If more than three apply to your environment, the conversation’s overdue.


The Blind Spot Session: A private session to see the risk your reports, your tools and your policies don't show. For CEOs, COOs, CFOs, IT leaders and compliance officers at PE-backed healthcare organizations
A Private Live Session
Every new location, system and vendor adds risk, and most growing healthcare organizations rarely get a CISO to look at it. The Blind Spot Session gives you 1 hour with one, built entirely around your role
You keep every location running and answer to the board. A plain-English read on where your operation is most exposed. What an hour of downtime costs you. What your board or insurer is likely to ask next.
You're the first to see the gaps and usually the last to get budget for them. A coverage check across your sites: MFA, EDR, backups, access to the EHR. Where your setup wouldn't hold up to an insurer questionnaire or an attacker. A plan you can take to leadership.
You see where what the policy says and what IT set up don't match. Whether your risk analysis is current and your BAAs are complete. Where your policies don't match the technical controls in place. How ready you are for the upcoming HIPAA Security Rule changes.
Private Workshop
A 1-hour Private Live Workshop Session with our CISO
Bring the one decision, project or finding that matters most to you right now.
Our CISO goes through your locations, systems and controls through the lens of your role.
We map the gaps: Where you're exposed: downtime cost for executives, coverage gaps for IT, policy-to-control gaps for compliance.
Your first 3 moves: What to fix first, and why.
Bring the one situation you want help with Rough facts: number of locations, sites added in the past year, the date of your last assessment, when your cyber insurance renews No patient data or credentials. We work at the level of architecture and policy.
Book Private WorkshopIn the meantime, you can take this free self-serve assessment about the proposed HIPAA Security Rule updates that introduce mandatory MFA, a 72-hour recovery time objective, and new documentation requirements.
Start AssessmentThe eight signs below indicate your business is ready for that shift. If more than three apply to your environment, the conversation’s overdue.
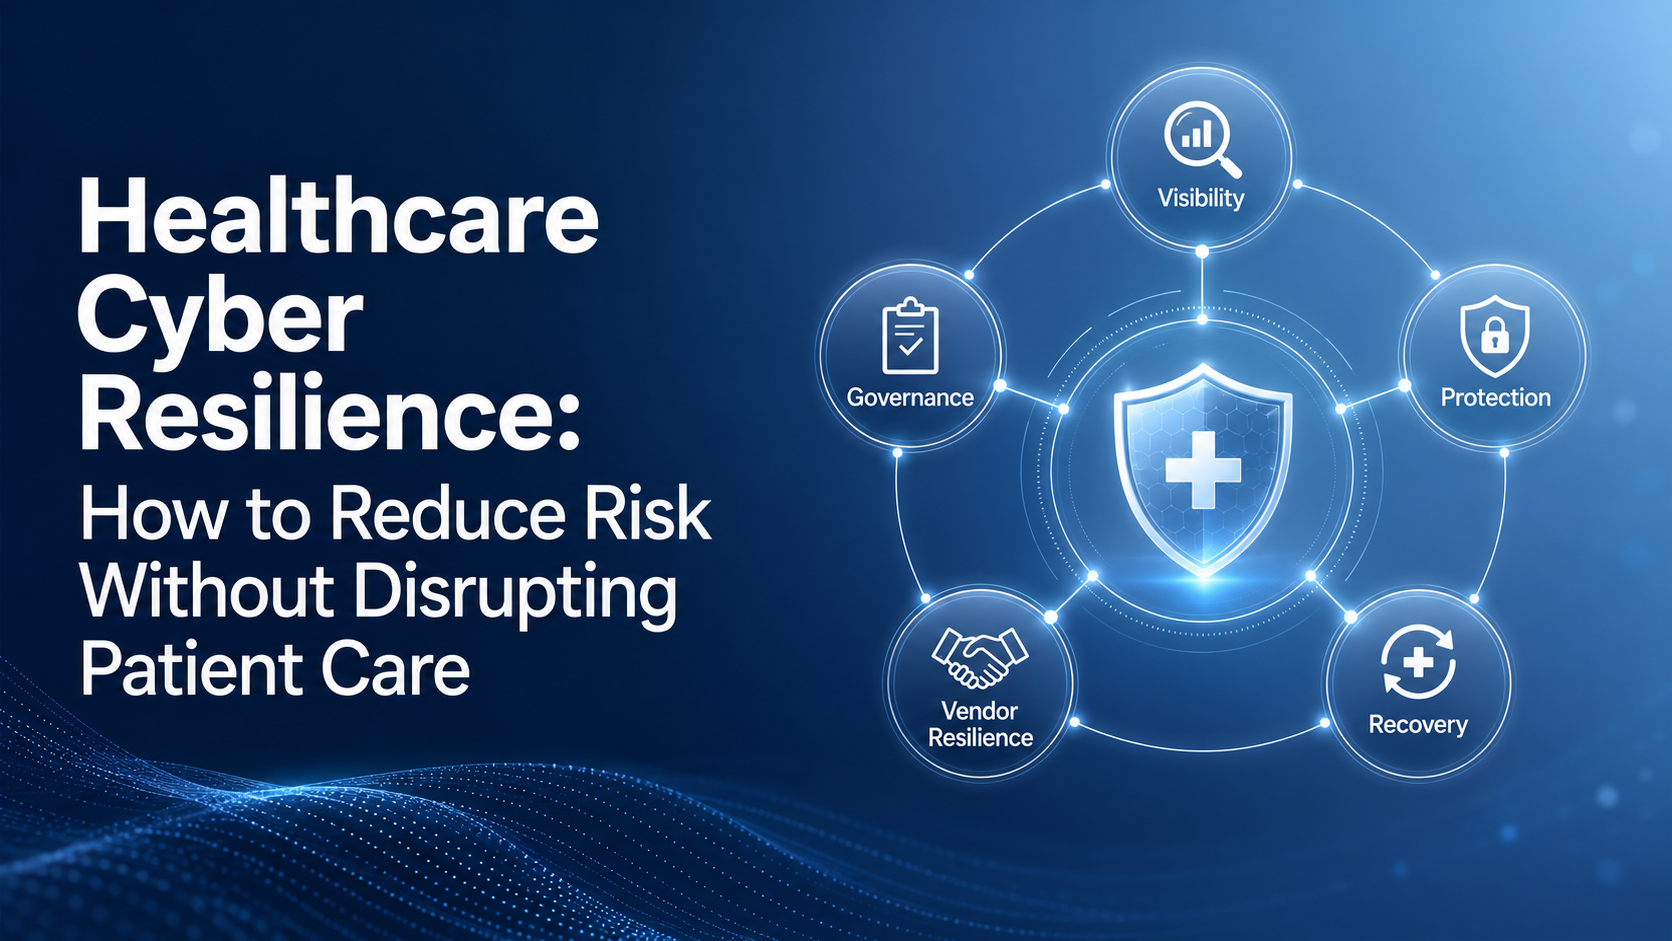
Healthcare cyber resilience is the ability to anticipate, withstand, recover from, and adapt to cyber disruptions while maintaining critical operations and supporting patient care.
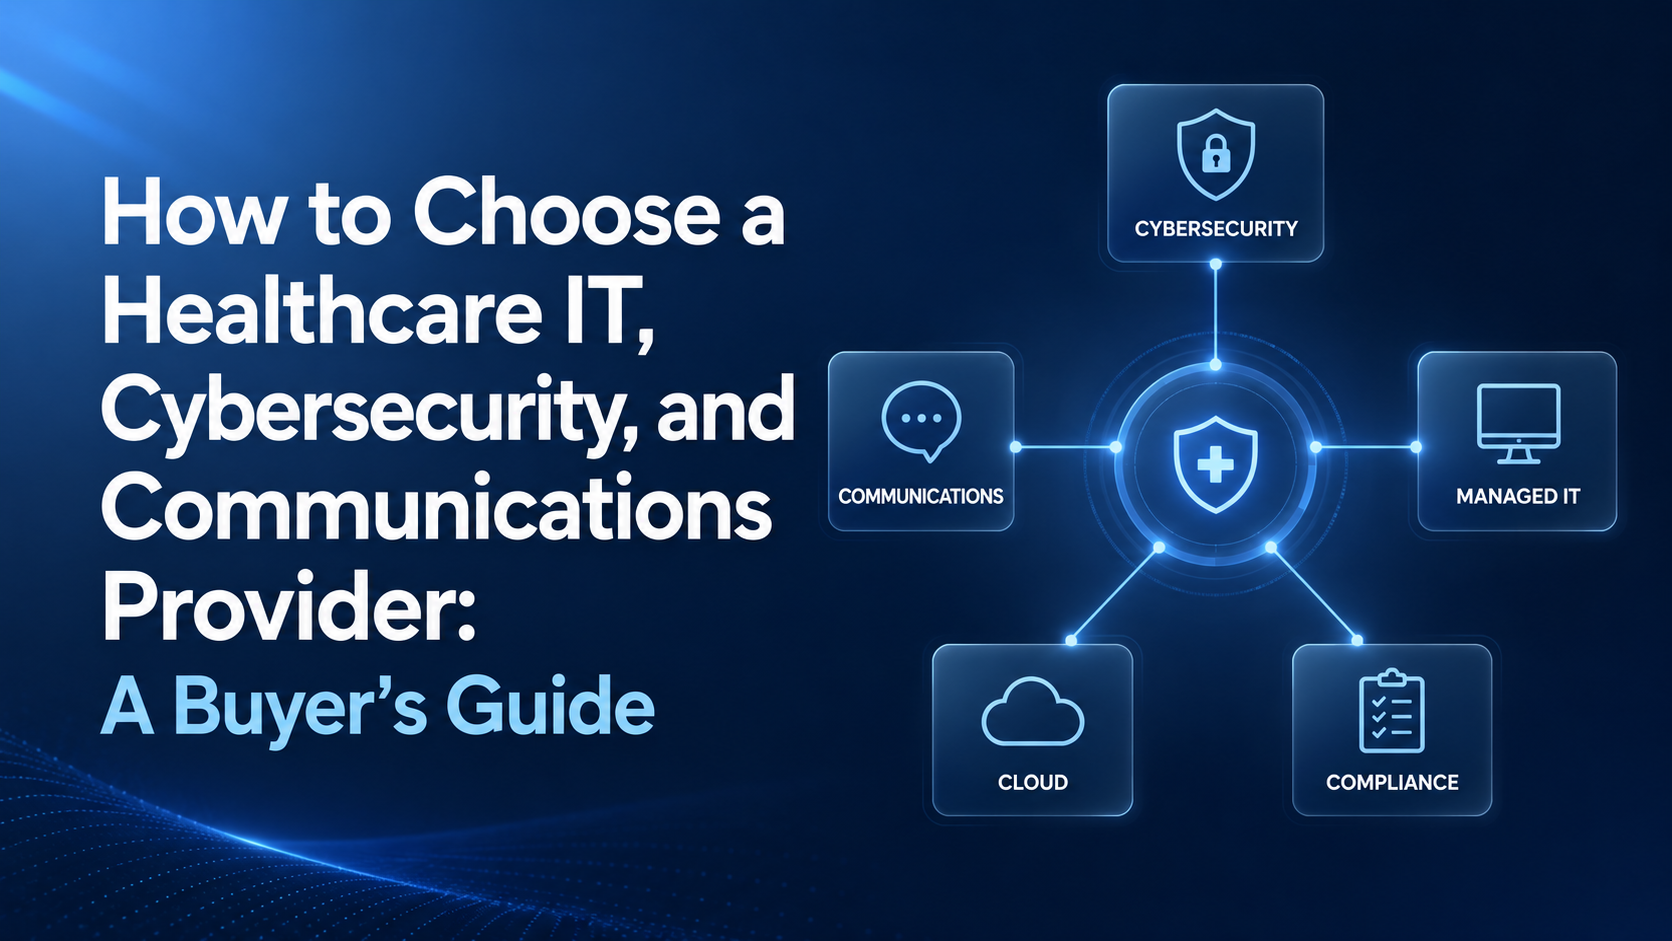
Price matters. Features matter. Service-level agreements matter. But none of those tell the full story. The better question is whether your provider can help your organization reduce risk, maintain continuity, support HIPAA readiness, and recover when technology does not behave as planned.